Independent GxP Auditing and AI Governance for Australian Pharmaceutical Teams
Built on 24 years of hands-on experience. Pharmacist. QPPV. ISO Lead Auditor. AI Practitioner, not just a consultant.
GxP Vigilance is an independent Australian consulting practice. We conduct risk-based GCP, GVP, and quality audits, design pharmacovigilance systems, and help pharmaceutical teams adopt AI that withstands regulatory scrutiny.
We build working systems and transfer the capability to run them. When an engagement ends, your team is equipped — not dependent on us to keep things running.
Why GxPVigilance Exists
Vendor oversight is now one of the highest-risk pressure points in GxP operations. External providers run critical activities, yet findings repeat, transparency varies, and internal oversight is stretched—while teams are expected to move faster without compromising compliance or patient safety.
At the same time, AI tools are entering pharmaceutical workflows faster than governance frameworks can keep up. Most teams know AI could reduce their manual burden. Very few have a defensible plan for doing so in a regulated environment.
GxP Vigilance exists to solve both problems. We audit how providers actually operate — not just what their SOPs claim — testing real-world governance: oversight models, data flows, documentation, training, escalation, CAPA effectiveness, and inspection readiness. We also help organisations adopt AI in a controlled way: validated workflows, clear ownership, documented controls, traceable outputs, and defined human approval points.
AI delivers value when it’s governed. Patient safety is non-negotiable. Independence is maintained. AI supports—humans approve. Capability is built, not outsourced.
What We Do
GxPVigilance provides independent GxP (GCP, GLP, GDP, CSV) auditing, pharmacovigilance consulting and AI-enabled transformation services across pharmacovigilance, clinical research, quality systems, regulatory affairs, manufacturing and data management. We serve pharmaceutical sponsors, CROs, investigator sites, and healthcare organisations across Australia, New Zealand, and APAC.
Our regulatory context is TGA-first, with full alignment to ICH harmonised guidelines and working knowledge of FDA and EMA expectations. We are not translating international frameworks — we build for the Australian regulatory environment.
Services
| Core service | What we do | Outcome |
|---|---|---|
GxP Auditing Services | Independent, risk-based audits across GCP, GVP, GLP, QMS and CSV/data integrity, focused on how work is actually performed—evidence, traceability, data integrity, and oversight in practice. | Clear, defensible audit outcomes aligned to TGA and ICH inspection expectations. Options: pre-audits, mock inspections, and CAPA support. |
Responsible AI Enablement | Governance-first AI adoption that delivers value safely: defined scope, human accountability, documented controls, auditable evidence capture, and inspection-ready ways of working. | Readiness assessments, governance framework design, validation/assurance, implementation support (PV/Reg, Clinical/Pharmacy specialties). |
Training & Capability Building | Practitioner-level enablement so teams can run and evolve systems independently—governance, oversight, privacy controls, and audit-ready execution. | AI governance, ISO/IEC 42001 (practical), human-in-the-loop oversight, safe AI use, AI-assisted GxP writing, validation thinking. |
PV System Design & QMS Integration | Regulator-aligned PV system design and independent audits that strengthen governance, traceability, and sustained compliance—especially where PV–QMS links drift over time. | QPPV governance models & metrics, PV–QMS integration (SOP/CC/CAPA), inspection readiness/defence, operational oversight, risk/regulatory support. |
GxPVigilance’s Values
Clarity — Plain-English guidance and clean artefacts so everyone knows what, why, and by when.
Control — Traceable, documented workflows with clear ownership so your team runs the system.
Confidence — Proof you can present, with reproducible results and full traceability.
Integrity — Patient safety first; human-in-the-loop, no shortcuts, no black boxes.
- Partnership — Co-designed, transparent, with capability transfer so you stay independent
- Authenticity — Practitioner-built, audit-tested solutions we would use in our own work.
What We Believe
Compliance should enable improvement, not fear.
AI is a tool for clarity, not a shortcut around responsibility.
Teams should own their systems — not rent dependency.
Transparency builds trust with regulators and patients.
- Expertise should be shared and built, not hoarded
- Patient safety remains non-negotiable
- Progress comes through partnership, not perfection.
Who We Are
GxPVigilance is an independent consulting practice led by Carl Bufe, a pharmacist, GxP auditor, and AI practitioner with 24+ years of hands-on experience across pharmacovigilance, quality systems, clinical research, pharmaceutical operations, and regulatory affairs.
Location & Scale
Based in Brisbane with a Sydney office, we serve regulated teams across Australia, New Zealand, and APAC. We work with trusted subject-matter partners and use client-approved AI providers (Microsoft 365 Copilot, Azure OpenAI, Anthropic, Google Gemini) to accelerate delivery and consistency—while keeping client data confidential and preserving audit independence.
AI Governance & Transparency
All AI-assisted work is ISO/IEC 9001, ISO/IEC 42001 and GAMP 5-aligned, with full traceability, human-in-the-loop review, and transparent documentation.
Meet Carl Bufe – Principal Consultant & Founder
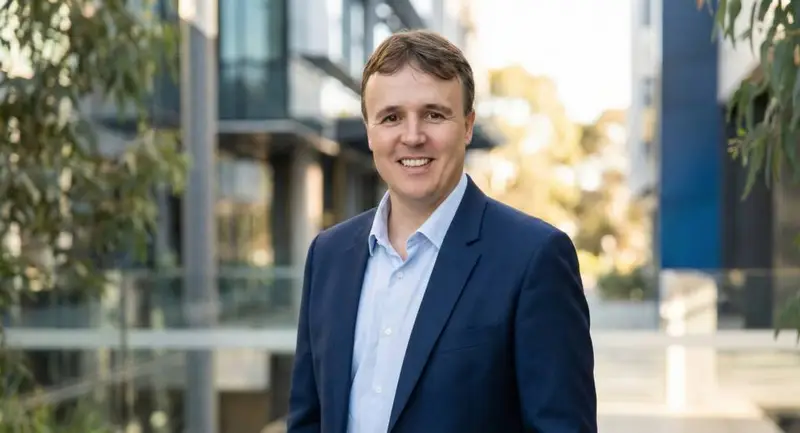
Pharmacist | QPPV | ISO Lead Auditor | AI Governance Practitioner
Carl Bufe founded GxP Vigilance on one observation: pharmaceutical teams needed someone who could build working GxP systems — not just assess gaps and write a report. After 24 years across pharmacovigilance, quality systems, GCP auditing, pharmacy practice, and clinical research, he built the practice around implementation, capability transfer, and AI governance done properly.
Career Summary
Carl’s 24 years span pharmacovigilance leadership, GCP auditing, quality system design, pharmacy practice, and AI governance — across clinical research organisations, pharmaceutical sponsors, hospitals, and healthcare systems. He has worked across Australia, New Zealand, and internationally.
Before founding GxP Vigilance, Carl held senior roles in quality, compliance, and pharmacovigilance at major CROs and pharmaceutical organisations. He has conducted GCP audits across Australia and internationally, designed and validated pharmacovigilance systems for TGA inspection readiness, led due diligence assessments for sponsors and CROs, and built AI governance frameworks that meet ISO/IEC 42001 and GAMP 5 requirements.
His work has directly supported TGA inspection preparation, FDA submission readiness, and EMA compliance across multiple therapeutic areas and sponsor types.
Expertise & Focus Areas
Pharmacovigilance and Safety Systems: A-PVCP and QPPV model design, ICSR workflows, signal detection and oversight, expedited reporting, safety database management, medical review coordination, and sponsor-investigator communication. Carl has designed and audited pharmacovigilance systems against TGA, GVP, and ICH E2A–E2F requirements.
GCP Auditing and Vendor Qualification: Independent sponsor and investigator site audits, vendor due diligence, TGA inspection readiness, ICH E6(R3) transition support, GCP systems assessment, and research operations quality review. Audit reports are written for inspection defensibility, not internal filing.
AI Governance and Implementation ISO/IEC 42001 and GAMP 5-aligned AI lifecycle management, AI-enabled pharmacovigilance and regulatory intelligence workflows, human-in-the-loop safety systems, and validation and testing protocols for LLM-based tools in regulated environments.
Quality Systems and Data Integrity QMS design, ALCOA+ data integrity, electronic records and audit trail review (COTS and custom systems), vendor assessment, and compliance strategy. Audit-ready documentation is produced at every stage.
Clinical Trial Operations Research operations quality, pharmacy and clinical manufacturing compliance, clinical supply chain oversight, study startup readiness. Practical experience across Phase I–IV studies.
Qualifications & Credentials
Professional Qualifications
- Bachelor of Pharmacy (Honours)
- Postgraduate Diploma in Quality Systems
- Bachelor of Commerce (Risk & Finance)
- Bachelor’s Information Systems
Auditor & Technical Certifications
- ISO Lead Auditor — ISO 9001 (Quality Management Systems)
- ISO Lead Auditor — ISO 13485 (Medical Devices Quality Management)
- ISO Lead Auditor — ISO/IEC 42001 (AI Management Systems) — the international standard for responsible AI governance in organisations
- Certificate in Computer System Validation (CSV)
- GCP Training — ICH E6 R2/R3, TGA and MHRA-aligned
- Pharmacovigilance Practitioner — A-PVCP/QPPV model experience
Professional Associations
- ARCS Australia — Australasian Regulatory and Clinical Sciences
- Pharmaceutical Society of Australia
- Advance Pharmacy Australia
- Life Sciences Queensland
- Queensland AI Hub
Published Articles
Carl writes on pharmacovigilance practice, GCP auditing, and AI governance in regulated environments. Selected articles:
What Makes GxP Vigilance Different
GxP Vigilance combines regulatory depth, implementation capability, and practical healthcare context so organisations can build compliant systems that work in the real world, not just in assessment reports.
Dual Mastery — GxP and AI in One Practice
Most compliance consultancies and most AI consultancies work in separate lanes. GxP Vigilance operates at the intersection, bringing governance, validation, and implementation together in one practice.
Carl holds ISO lead auditor credentials across quality management, medical devices, and AI management systems, alongside active QPPV and pharmacist registration. That means fewer handoffs, less translation loss, and one accountable partner across both domains.
Implementation Focus, Not Assessment-Only
A gap analysis without a working system to show for it is a report that sits in a folder. Every GxP Vigilance engagement is designed to produce something operational, whether that is a validated workflow, a practical SOP set, a trained team, or a documented governance framework.
Findings come with fixes so the result is usable in practice, not just defensible on paper.
Patient Safety Non-Negotiable
Every AI tool, every efficiency gain, and every audit recommendation traces back to one question: does this protect the patient? Human oversight is treated as a regulatory control, not an optional layer added at the end.
That principle does not change because of delivery pressure, resource constraints, or programme timelines.
Pharmacist and Builder — Not Just Consultant
Carl maintains active pharmacy registration and works clinical shifts. That keeps the practice grounded in how healthcare actually operates, not just how it appears in a framework document or slide deck.
It also means current regulatory expectations are lived knowledge rather than archived reference material. The advice is practical because the context is real.
Australian TGA Context, Built-In
The practice is designed for the Australian regulatory environment from the outset. TGA requirements, local sponsor obligations, APAC vendor oversight, and Trans-Tasman alignment are not retrofitted from global templates.
They are the starting point for how the work is structured, documented, and implemented.
Training-First Approach — Capability Transfer, Not Dependency
Every engagement includes a deliberate knowledge transfer component. The objective is not to create dependence on an external consultant, but to leave the client team able to run, maintain, and improve their systems independently.
If you need to call us every time something changes, the engagement has not gone far enough. Capability transfer is part of the deliverable.
Who We Work With
GxP Vigilance works with:
- Australian pharmaceutical sponsors managing TGA obligations, local pharmacovigilance systems, and GCP-compliant clinical programs
- Contract Research Organisations (CROs) requiring independent vendor qualification audits, GCP oversight, or AI governance for clinical data systems
- International sponsors needing APAC-based auditing and vendor oversight across Australia, New Zealand, and the broader region
- Hospitals and investigator-initiated study teams are building GCP-compliant trial infrastructure and inspection readiness
- Pharmaceutical distributors and importers with TGA compliance and pharmacovigilance obligations
- Healthcare organisations implementing AI tools in regulated clinical or quality environments
Location and Scale
Based in Brisbane, Queensland, with an office in Sydney, New South Wales. We serve regulated teams across Australia, New Zealand, and APAC — remote, on-site, or hybrid depending on engagement type and client preference.
We work with trusted subject-matter partners for specialist requirements and use client-approved AI providers — Microsoft 365 Copilot, Azure OpenAI, Anthropic, Google Gemini — to accelerate delivery while keeping client data confidential and preserving audit independence.
AI Governance and Transparency All AI-assisted work is aligned to ISO/IEC 9001, ISO/IEC 42001, and GAMP 5, with full traceability, human-in-the-loop review at defined approval points, and transparent documentation of where and how AI has been used.
Testimonials
GxPVigilance helped us clear a 2-month backlog in 2 weeks.
Australian Biotech
The questions below come up most often in scoping calls — what a GxP audit actually assesses, what Australian sponsors are obliged to do, and what governed AI adoption looks like in a regulated environment.
What does a GxP auditor do in Australia?
A GxP auditor independently assesses how regulated activities are actually performed, not what the procedures claim. In Australia that covers Good Clinical Practice (GCP) for clinical trials, Good Pharmacovigilance Practice (GVP), Good Laboratory Practice (GLP), and the quality management system holding them together.
The TGA expects sponsors to maintain oversight of the activities they contract out. An independent audit is one of the few ways to discharge that obligation with evidence rather than assurance.
We audit against ICH E6(R3) and TGA inspection expectations, and we write findings to the standard an inspector would apply — evidence, traceability, escalation, and whether CAPA actually worked. You get findings with realistic closure timelines, not a report to file.
Do Australian pharmaceutical sponsors need a QPPV?
No. Australia has no QPPV requirement equivalent to EU GVP Module I. That does not reduce the underlying obligation.
Sponsors holding ARTG entries remain responsible for operating a pharmacovigilance system and meeting TGA safety reporting timeframes. Most appoint an Australian Pharmacovigilance Contact Person (A-PVCP) to hold TGA correspondence and local reporting.
We design A-PVCP arrangements and QPPV-aligned governance for sponsors carrying international obligations. Where we hold the role, it comes with active oversight — metrics, escalation paths, and documented decisions — not a name on paper.
What is AI governance in a GxP environment?
AI governance is the documented answer to three questions a regulator will ask: who approved this system, how do you know it works, and what happens when it gets something wrong.
In practice that means defining which tools are used, for what purpose, under what controls, with which human approval points, and how outputs are reviewed and retained as records. ISO/IEC 42001 and GAMP 5 (Second Edition, including Appendix D11) are the frameworks we work to. The work covers risk classification of each use case, human-in-the-loop design, audit trail requirements, change control for model updates, and validation evidence.
Governance before automation. Human oversight before scale.
What is the difference between GCP and GVP auditing?
GCP auditing looks at how a clinical trial is run — design, conduct, documentation, delegation, and oversight against ICH E6(R3) and TGA expectations. GVP auditing looks at the safety system — how adverse events are captured, assessed, reported within timeframes, reconciled, and followed up.
They fail in different ways. A trial can be well run and still carry a safety reporting gap; a safety system can be sound while site oversight drifts. Sponsors with obligations in both areas need both assessed.
We run them separately, or as one combined programme where the same vendors and systems sit behind both.
How long does a pharmacovigilance system audit take?
Plan on two to four weeks end to end. The assessment itself is short — typically one to two days, remote or on-site — but the schedule around it determines the date.
We lock the agenda two weeks before an on-site audit, or two and a half to three weeks for remote and complex audits, with the document request issued a week ahead. Tentative findings are discussed at close-out on the day. The draft report is issued within ten working days, and you have five to ten working days for factual accuracy review before the final report.
Scope, the number of contracted providers in the chain, and how much evidence the auditee has ready are what move that timeline. CAPA remains yours to own; plan review, monitoring, and effectiveness verification are available as separate tiers if you want support closing it.
What does ‘human-in-the-loop’ mean for AI in pharmaceutical operations?
It means a qualified person reviews and approves any AI-generated output before it becomes part of a regulated record or decision.
Treat it as a regulatory control rather than a precaution. TGA, ICH and GAMP 5 all expect documented human accountability for decisions affecting product quality and patient safety, and “the system generated it” is not a defensible answer at inspection.
We build the approval points into the workflow itself — who reviews, at what stage, against what criteria, with the decision logged. AI supports — humans approve.
What is ICH E6(R3) and how does it affect Australian clinical trials?
ICH E6(R3) is the current Good Clinical Practice guideline. It moves GCP from prescriptive compliance toward risk-proportionate quality — critical-to-quality factors identified up front, quality management built into the protocol, and explicit expectations for data governance across electronic systems.
The TGA recognises ICH guidelines and expects Australian sponsors and CROs to be operating to current E6 expectations. The practical effect is that a monitoring plan or oversight model designed under R2 will not automatically satisfy an R3 assessment.
We audit against E6(R3) and support sponsors working through the transition, including where legacy studies and R2-era vendor agreements are still running.
Disclaimer
This article is provided for educational and informational purposes only. It is intended to support general understanding of regulatory concepts and good practice and does not constitute legal, regulatory, or professional advice.
Regulatory requirements, inspection expectations, and system obligations may vary based on jurisdiction, study design, technology, and organisational context. The information presented here should not be relied upon as a substitute for project-specific assessment, validation, or regulatory decision-making.
We have no commercial relationship with any of the entities, vendors, or software referenced in this article. Any examples are illustrative only and may not reflect your organisation’s specific requirements or context.
Last reviewed
GxP Vigilance
Questions specific to your programme?
A 30-minute scoping call costs nothing and leaves you
with a clear picture of where you stand.
